
Lappa Security & Trust
Learn how Lappa protects your compliance data through security practices, data protection measures, and an ISO/IEC 27001:2022-certified information security management system
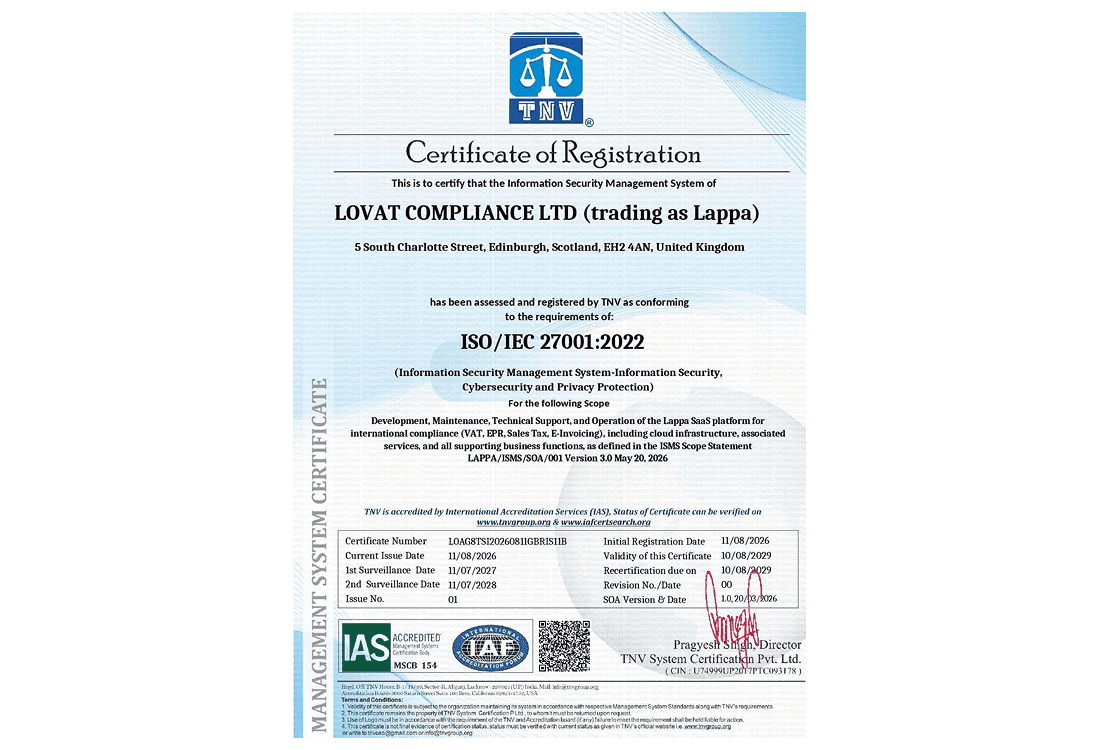
- ISO/IEC 27001:2022 certified
- GDPR & privacy focused
- Designed for global businesses
Your data, your trust.
We are committed to protecting personal and business data in accordance with the General Data Protection Regulation (GDPR) and other applicable data protection laws.


Independently certified. Clearly documented.
Lappa’s information security management system (ISMS) has been independently certified to ISO/IEC 27001:2022, supporting our commitment to protecting customer data and maintaining robust security practices.
ISO/IEC 27001:2022 Certification Details
Lovat Compliance Ltd (trading as Lappa) holds ISO/IEC 27001:2022 certification for its Information Security Management System (ISMS). The certification covers the development, maintenance, technical support, and operation of Lappa's SaaS platform for international compliance.
|
Certification details |
Information |
|---|---|
|
Certification standard |
ISO/IEC 27001:2022 — Information Security Management Systems |
|
Certified organization |
Lovat Compliance Ltd (trading as Lappa) |
|
Certification body |
TnV (TNV System Certification Pvt. Ltd.) |
|
Accreditation body |
International Accreditation Service (IAS) |
|
Initial certification date |
11 August 2026 |
|
Certificate valid until |
10 August 2029 |
|
Scope of certification |
Development, maintenance, technical support, and operation of the Lappa SaaS platform for international compliance (VAT, EPR, Sales Tax, E-Invoicing), including cloud infrastructure, associated services, and supporting business functions. |
|
ISMS scope reference |
LAPPA/ISMS/SOA/001, Version 3.0 — 20 May 20 |
Built with security at every layer.
Encryption in transit
Data is protected during transmission between your browser, our services and internal systems.
Encryption at rest
Customer data is protected at rest within our infrastructure environment.
Identity & access control
Access to systems and data is managed based on roles and the principle of least privilege.
Multi-factor authentication
MFA is used to protect administrative and sensitive accounts.
Security monitoring
We monitor our systems and processes to detect and respond to potential security risks.
Vulnerability management
We follow a structured process for identifying, assessing and remediating vulnerabilities.
Secure infrastructure
Our platform is built with a focus on secure infrastructure and operational best practices.
Third-party assurance
We review third-party service providers and consider their security practices as part of our due diligence.
Incident Response
Detect
Monitor systems and identify signals of a potential incident or anomaly.
Assess
Evaluate severity, affected systems and business impact according to internal procedures.
Respond
Contain and manage issues; communicate and notify where required by law or contract.
Security questions, answered.
Yes. Lovat Compliance Ltd, trading as Lappa, holds ISO/IEC 27001:2022 certification issued by TnV, with the certificate shown is valid from 11 August 2026 until 10 August 2029.